Ahead through knowledge and experience
More topics:ISO 27001ISO 27701TISAXNIS-2CADISISO 22301OT-SecurityCRADefence
DEENESFR
NIS2
NIS2 has applied in Germany since 6 December 2025: check in 2 minutes whether you are affectedBSI registration deadline expired on 31 July 2026: not registered yet? We help immediatelyManagement is personally liable and must be trained (§ 38 BSIG)Reporting duty: early warning within 24 hours, notification within 72 hours, final report after one month (§ 32 BSIG)Fines up to €10 million or 2% of worldwide turnover (§ 65 BSIG)CONSUVATION: the NIS2 solution built on knowledge, experience and a platform

GRC platform for ISO 27001, NIS2, TISAX, AI, BCM, CADIS (defence), CRA, OT and complianceKnowledge and experience, not just software. Compliance by experts, delivered pragmatically. For SMEs, mid-sized companies and corporate groups.

NIS2TISAXData protectionISO 27001AI ActCRACADIS

The CONSUVATION GRC Platform is backed by experts who help shape ISO standards and audit as auditors for certification bodies. That is why the platform asks for exactly what the requirements demand and what is sensible and necessary, and nothing more. Small and mid-sized companies reach certification with lean documentation and without their own security department. And the result stands up in the audit.

  • Knowledge and experience, not just a software solution
  • Experts and auditors from project to operations
  • Multi-tenant for corporate groups with subsidiaries

Example: maturity level per framework

ISO 2700186%
NIS2 Art. 2174%
ISO 2770168%
TISAX / VDA ISA61%
ISO 2230142%

Illustrative sample values. One implemented control counts towards every linked framework.

Auditors for certification bodies: ISO 27001, 27701, 22301, 9001Members of ISO standardisation committeesCISA · CISM · CRISC · CGEITOver 25 years of experienceOfficial DEKRA partner for CADIS
We are the officer company. External officers from a single source: CISO, DPO, NIS2, AI and TISAX.
More than software

Knowledge and experience, supported by software

Software alone does not make a company audit-ready. Knowledge and experience make the difference: standards expertise from the ISO committees and more than 25 years of auditing and consulting. The platform is our tool; our experts support you across the entire cycle, from the initial project to ongoing operational support.

Standards knowledge first-hand

Our consultants sit on the ISO committees for ISO 27001 and ISO 27701. New editions of the standards are in the tool before others start interpreting them.

Through the auditor's eyes

Controls, evidence requirements and audit questions come from our practice as auditors for certification bodies.

Implement once, prove many times

A shared control model links ISO standards, NIS2, GDPR and industry standards. One piece of evidence covers several requirements.

Experts who deliver

On request, we take on the role of external CISO or DPO and work directly in your platform, remotely or on site.

Made for SMEs

Platform plus operational support from experts

Many small and mid-sized companies need a certificate or have to comply with NIS2, but have neither a CISO nor a data protection team. The platform is built for exactly this situation, together with our operational support. Our experts create the documents, maintain risks and measures in the platform, handle the annual tasks and prepare you for the audit. You decide and approve. We do the work.

  • NIS2 without the full build-out: a standalone NIS2 solution for small companies, without a full ISO 27001 or TISAX implementation
  • Lean documentation: only the documents the standard and the auditor actually require
  • Fast start: pre-filled templates, risks and measures instead of blank forms
  • Operational support: CISO, DPO and AI Officer from our team who work in the tool, with no extra headcount
  • Already have an internal CISO or DPO? Then we support them with expertise and hands-on help
  • Predictable effort: fixed packages and an annual calendar that shows what is due when
  • Personal: a dedicated contact who knows your company
NIS2 solution

Meeting NIS2: we deliver the solution, not just software

Germany’s NIS2 Implementation Act has applied since 6 December 2025. Software alone does not fulfil any of these obligations. Our experts and auditors implement NIS2 with you; the platform makes every step verifiable.

1 · Scope and registration

We assess your classification under § 28 BSIG and handle registration with the BSI, even though the deadline of 31 July 2026 has passed.

2 · Risk management under § 30 BSIG

A proven NIS2 risk model and 64 NIS2 documents in 9 categories are ready to use. Our experts implement the measures with you.

3 · Reporting and management duties

Reporting process for 24 hours, 72 hours and one month under § 32 BSIG, plus the mandatory management training under § 38 BSIG.

4 · Ongoing support

External NIS2 officer, annual calendar and evidence for the BSI, customers and management, all available in the platform.

Standalone NIS2 solution for SMEs, without full ISO 27001 or TISAX. Obligations, deadlines, sectors, liability and fines in detail: nis2-richtlinie.de

NIS2 self-check

Does NIS2 apply to your company?

Three questions, an instant result. The check is based on the German NIS2 Implementation Act and is not legal advice. Linked and partner enterprises count towards company size.

1. In which sector does your company operate?
2. How large is your company?
3. Does one of these special cases apply?

Operator of a critical facility (KRITIS), qualified trust service provider, TLD registry, DNS service provider, provider of public telecommunications networks or services

Your result

Answer the three questions. Your result will appear here.

Discuss your result with an expert
Full cycle

From project to operational support

We deliver more than a tool. In every phase, experts and auditors work with you, from the first project through certification to ongoing operations. The platform keeps everything together.

1

Project kick-off and gap analysis

Determine the scope, applicability (for example under NIS2) and maturity level per framework.

Experts
2

Build and implementation

We create documents, risks and measures with you directly in the platform.

Experts
3

Verify effectiveness

Internal audits and management review through the eyes of a certification auditor.

Auditors
4

Certification

Audit preparation, coordination with the certification body and support during the certification audit or TISAX assessment.

Experts and auditors
5

Operational support

External CISO, DPO and AI Officer, annual calendar, legal monitoring, surveillance audits.

Experts
Solutions

Tailored to your starting point

A machine builder with a production network has different obligations from a software company or a research institute. That is why we start with your industry, not your company size.

SMEs and mid-sized companies

No in-house security team, but customers demand ISO 27001 and NIS2 may apply to you.

  • NIS2 applicability check and registration
  • Standalone NIS2 solution without full ISO 27001 or TISAX
  • ISMS with preconfigured templates
  • External CISO and DPO from a single source
  • A dedicated contact instead of a ticket system
ISO 27001 · NIS2 · GDPR

Industry and OT

Production plants, control systems and remote maintenance belong in scope, but do not fit classic IT catalogues.

  • Zone and conduit model according to IEC 62443
  • OT assets and risks in the same tool as IT
  • Product regulation under RED/RCE
  • BSI IT-Grundschutz as a supplement
IEC 62443 · NIS2 · RED

Automotive supply chain

OEMs require TISAX labels, often at short notice.

  • TISAX consulting and TISAX assessors based on VDA ISA
  • Scope extension to additional sites
  • Prototype protection and data protection modules
  • Reuse of evidence for ISO 27001
TISAX · VDA ISA · ISO 27001

Corporate groups and critical infrastructure (KRITIS)

Several entities, sites and management systems need consistent governance and reporting.

  • Integrated management system across ISO 27001, 22301, 9001, 37301
  • Multi-tenant for parent company and subsidiaries
  • Group-wide supplier management
  • Reports for the management board and statutory auditors
IMS · ISO 22301 · ISO 37301

Research and academia

Open networks, changing project teams and research data subject to funding requirements.

  • ISMS for distributed sites
  • RoPA templates for research projects
  • Data protection according to ISO 27701
  • AI governance according to ISO 42001
ISO 27001 · ISO 27701 · ISO 42001

Internationally active companies

Data protection and security requirements differ by country and customer.

  • Documentation in German, English and other languages
  • Swiss nDSG (FADP) and other jurisdictions
  • NIS2 implementation in all EU countries and for companies outside Europe, for example from the US, that operate in the EU market
  • One management system for all sites
  • ISO 27001 and TISAX in Europe and the US
GDPR · nDSG · NIS2

Defence and armaments

Clients demand classified information protection, VS-NfD-compliant IT and export control, often on top of ISO 27001.

  • Requirements map from law and customer specifications
  • Classified information protection and VS-NfD-compliant processes
  • Export control within compliance management
  • Reuse evidence for ISO 27001 and NIS2
  • Quality management to EN 9100 and NATO AQAP
  • CADIS as an official DEKRA partner
More on defence market access →
CADIS · VS-NfD · EN 9100

Healthcare

Medical practices, care centres and hospitals process health data and must prove statutory IT security.

  • KBV IT security guideline under § 390 SGB V for medical practices
  • IT security in hospitals under § 391 SGB V
  • Protection of health data under Art. 9 GDPR
  • NIS2 for entities in the health sector
More on the KBV IT security guideline (DE) →
§ 390 SGB V · GDPR · NIS2

Manufacturers of connected products (CRA)

The Cyber Resilience Act applies to all products with digital elements on the EU market, including manufacturers outside the EU. Reporting obligations have applied since 11 September 2026, all obligations from 11 December 2027.

  • Determine applicability and product class, conformity assessment through to CE marking
  • Security by design and by default in development
  • Vulnerability management with SBOM and updates over the support period
  • Reporting process for exploited vulnerabilities and incidents: 24 h, 72 h, 14 days or 1 month
  • Aligned with IEC 62443, RED and ISO 27001
CRA · IEC 62443 · RED
International

ISO 27001, TISAX and NIS2 in Europe and the US

One management system for all sites, ISO 27001 as the baseline with country-specific standards, NIS2 in every EU country and for non-EU companies supplying Europe, and international legal monitoring.

Go to International
Platform modules

Everything for security and compliance in one place

All modules draw on the same assets, risks and evidence. Nothing is maintained twice.

Security
ISMS managementStatement of Applicability (SoA), objectives, management review
Asset managementProtection need, risk assessment, BCM parameters such as RTO/RPO, contingency plans
Risk managementOur own risk models per ISO 27005, § 30 BSIG and for AI, treatment plans
Measures and tasksManage operational tasks for CISO, DPO and departments throughout the year, continual improvement action list, deadlines, responsibilities, effectiveness reviews
Supplier managementSupplier risk analysis by criticality, automatic assessment against standards, automatic questionnaires, audits
Audit managementAudit programme, checklists, findings
Business continuityBIA and emergency plans according to ISO 22301
OT securityZones and conduits according to IEC 62443
Document controlCreation, review, approval, versioning, need-to-know with read confirmation
Visitor managementRegister and document visitors per site
E-learning and awarenessTailored training per system, awareness e.g. on ransomware, final test and automatic certificate
Guides and checklistsPublish guides and checklists for departments and employees, targeted by need-to-know
Compliance and data protection
AI assistanceAI creates drafts of the RoPA and asset register, our experts review them
Whistleblowing systemConfidential reporting channel and case handling under the German Whistleblower Protection Act (HinSchG)
Record of Processing Activities (RoPA)Processing activities under Art. 30 GDPR
TOMs according to SDM and ISO 27701Technical and organisational measures aligned with the SDM protection goals and the ISO 27701 controls
DPIAData protection impact assessment with risk evaluation
Data subject requestsAccess, erasure, deadline tracking
Data breaches and incidentsReporting processes for GDPR, NIS2 and information security with automatic deadline calculation (e.g. 72 h GDPR, 24 h / 72 h / 1 month NIS2) and reporting channels
Compliance managementObligations register and CMS according to ISO 37301
AI governanceAI register, risk classes, roles and approvals under the AI Act and KI-MIG, AIMS according to ISO 42001
Annual calendar for CISO and DPOMandatory tasks with deadline and evidence
Legal registerInternational legal monitoring with deadlines
KPI dashboard and reportingFreely configurable KPIs for data protection, ISMS and NIS2 with sample KPIs, maturity level per framework, reports for senior management

How everything connects

Sites, assets, processes, risks and evidence are linked in one data model. You see at a glance what a change affects.
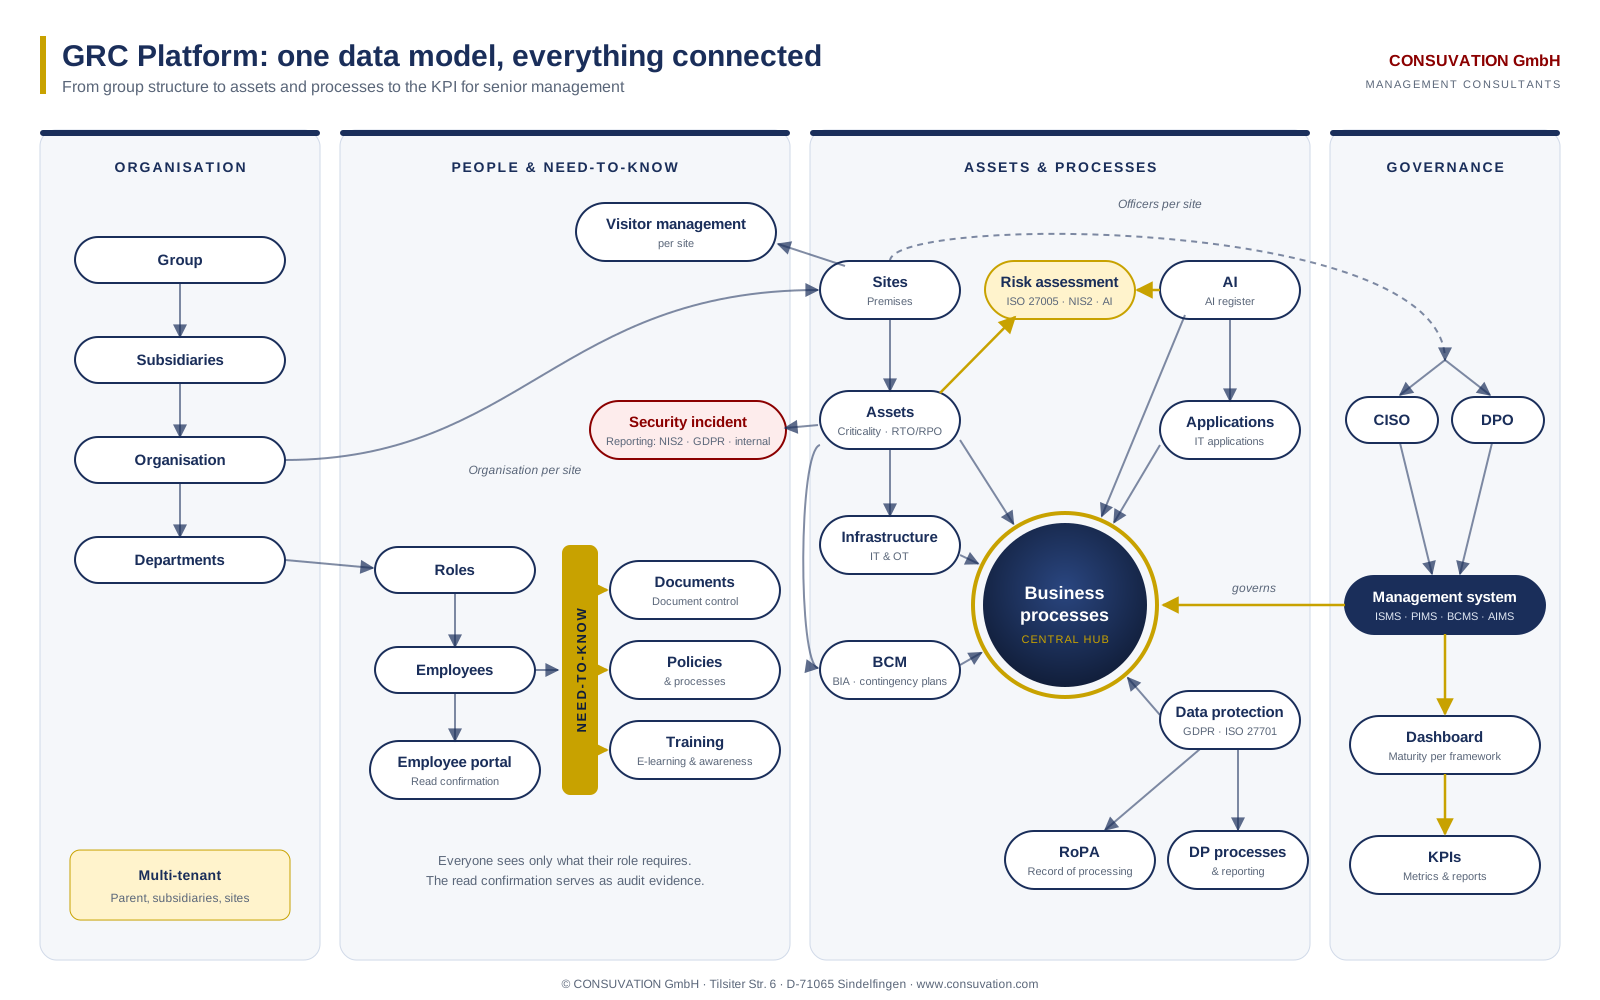
Structure model of the CONSUVATION GRC Platform: organisation, people and need-to-know, assets and processes, governance

Open graphic in full size

Document control

Creation, review, approval and versioning of all documents. Distribution follows need-to-know, with read confirmation.

Automated incident reporting

Data protection and security incidents run through automated processes with the right reporting channels under GDPR, NIS2 and information security requirements. The platform calculates the reporting deadlines automatically.

Everything at the asset

Each asset carries its risk assessment, BCM parameters such as RTO and RPO, and the contingency plans.

What else sets us apart

Tailored e-learning

No off-the-shelf courses. For every system we create tailored training, such as specific end-user training, exactly as auditors require. For awareness we use proven courses, for example on ransomware.

  • Formats: training courses, videos and microlearning, voiced in German and English
  • Final test to measure effectiveness
  • Fully automated from course delivery to certificate creation and dispatch

Strictly need-to-know

Employees see only the policies and processes they need for their work and confirm that they have read them. The read confirmation is your evidence in the audit.

Visitor management per site

Visitors are registered and documented per site directly in the platform, with no extra tool.

Automatic supplier assessment

A supplier risk analysis by criticality sets the depth and frequency of reviews. The platform assesses suppliers automatically against the relevant standards and, if you wish, sends supplier questionnaires automatically.
Platform security

Hosting in GermanyStrict tenant separationMulti-factor authentication (MFA)Encryption of your data
Risk management

Our own risk models: faster results, audit-proof

Risk assessment is a core requirement of every management system standard and a key focus in audits. We have developed our own proven risk models and processes and built them into the platform.

ISO 27005

ISMS based on ISO/IEC 27005

Asset-based risk assessment with protection need, threats and vulnerabilities, aligned with ISO 27001 clauses 6.1 and 8.2.

NIS2

NIS2 under § 30 BSIG

Risk management measures for essential and important entities, demonstrable to the BSI and senior management.

AI

AI under the AI Act and ISO/IEC 42001

Risk classification and impact assessment for AI systems, linked to the AI register and assets.

Supply chain

Suppliers

Risk-based supplier assessment with automatic questionnaires and fixed review cycles.

AI × information security

AI risks to information security

Our own risk model assesses how the use of AI endangers information security: 13 risk areas from shadow AI to in-house LLM applications and agents and AI in production, with 76 sample risks and 70 measures from 42 verified sources.

To the AI risk analysis →
In the platform:Risk matrix and acceptance criteriaTreatment plans with owners and deadlinesLinked to assets, BCM and measuresRisk report for senior management

The result: implementation is much faster and audit-proof.

Content included

Ready-made document libraries instead of blank templates

The platform comes with documentation landscapes that we built in client projects and proved in audits. Every document is typed as a policy, work instruction or evidence and is available in German and English. Further language versions exist.

50ISO/IEC 27001:2022ISMS policies and evidence
64NIS2in 9 categories
64ISO 37301Compliance management
60OT-SecurityIEC 62443, 12 CSMS categories
33ISO 22301Business continuity
35Swiss nDSGSwiss data protection (FADP)
20ISO/IEC 42001AI management system
117CISO annual calendarrecurring tasks with evidence, plus the DPO calendar

Number of documents per library, each in German and English, other languages available. For the annual calendar: number of recurring tasks.

Annual calendar for CISO and DPO

Both officer roles have fixed duties throughout the year. The platform schedules every task with a deadline, an owner and the evidence an auditor wants to see. Excerpt:

RoleQ1Q2Q3Q4
CISOUpdate risk assessment, prepare management reviewInternal audit, awareness campaignEmergency drill, supplier evaluationReview of the Statement of Applicability, audit planning
DPOActivity report to senior management, RoPA reviewData protection training, review of TOMsReview processors, deletion conceptDPIA review, annual planning
Frameworks

More standards than software alone can cover

Beyond the usual frameworks, we cover requirements from OT, the automotive industry, the defence industry and product regulation. For every framework, we advise on implementation and verify effectiveness as auditors.

ISO/IEC 27001Information security
Consulting Auditor for certification bodies
ISO/IEC 27701Privacy information management system
Consulting Auditor for certification bodies
ISO 22301Business continuity
Consulting Auditor for certification bodies
ISO 9001Quality management
Consulting Auditor for certification bodies
CADISCybersecurity for defence industry suppliers
Consulting Auditor for certification bodies DEKRA partner
NIS2 / NIS2UmsuCGApplicability, Art. 21 measures, reporting obligations; dedicated SME solution
Consulting Audit
TISAX / VDA ISAInformation security, prototype protection, data protection
Consulting TISAX assessors
GDPR and SDMExternal DPO, standards-based
Consulting Audit
ISO 31000Risk management
Consulting Audit
ISO 37301Compliance management
Consulting Audit
IEC 62443 / BSI IT-GrundschutzOT security
Consulting Audit
EU AI Act / KI-MIGAI compliance and market surveillance
Consulting Audit
ISO/IEC 42001AI management system
Consulting Audit
Defence and armamentsClassified information protection, VS-NfD (German classified information – restricted), export control, customer requirements, EN 9100, NATO AQAP
Consulting Audit
HinSchGWhistleblower protection, EU Whistleblowing Directive
Consulting Platform
RED / RCECybersecurity of radio equipment
Consulting Audit
AI compliance

EU AI Act and KI-MIG: use AI with legal certainty

Since 29 July 2026, the Federal Network Agency (Bundesnetzagentur) has been supervising compliance with the AI Act in Germany. We bring your use of AI into an auditable management system: AI inventory, risk classification, AI literacy under Art. 4, AI governance, an external AI Officer and ISO/IEC 42001.

Go to the AI compliance page
Comparison

What you get on top with us

Software alone does not make a company audit-ready. The difference lies in what stands behind the tool.

CriterionTypical SaaS compliance providerCONSUVATION GRC Platform
Contribution to ISO 27001 and ISO 27701Implements published standards✓ Active members of the standardisation committees
Auditor perspectivePreparation for the audit✓ Auditors for certification bodies for ISO 27001, 27701, 22301, 9001
OT, automotive and defenceOften not covered✓ IEC 62443, CADIS, TISAX with our own assessors, RED/RCE
External data protection officerMostly checklist-based✓ Standards-based according to ISO 27701 and SDM, with a law firm partnership
Cross-framework evidenceDepends on the product✓ One control model, evidence counts towards every framework
On-site implementationMainly remote✓ Remote and on site, dedicated contacts
Consultant qualificationsOften described vaguely as “certified”✓ Named openly: CISA, CISM, CRISC, CGEIT, auditor accreditations
Document librariesTemplates to fill in yourself✓ Audit-proven documentation landscapes in German, English and other languages
Solutions by industrySegmented by company size✓ Dedicated packages for OT, automotive, critical infrastructure, research
Coordination with certification bodiesYour job✓ We handle it, thanks to close contacts with the certification bodies
TrainingOften standard courses✓ Tailored end-user training per system, as required in audits
Access to policiesOften every document for everyone✓ Strictly need-to-know with read confirmation
AI supportYou review AI results yourself✓ AI creates drafts, for example the RoPA and asset register, and experts review them
IT audit for the annual financial statementsNot part of the offering✓ IT auditors with CISA qualification

The middle column describes offerings that are common in the market and does not refer to any specific provider.

Results, not stories

We don't tell stories. We deliver.

Anonymised project examples with scope and outcome, from ISMS to OT security.

See the results
Our three roles

Standard setter, auditor and implementer

This combination is rare in the market. It shapes how our platform is built.

Standard setter

We contribute to ISO 27001 and ISO 27701 and know the intent behind every requirement.

ISO 27001ISO 27701

Auditor

As auditors for certification bodies, we audit management systems. We also carry out our own audits under NIS2, GDPR, the AI Act, IEC 62443 and other frameworks. We know which evidence holds up.

Certification bodiesISO 22301ISO 9001CADISTISAX

Implementer

We build management systems, take on CISO and DPO roles and support ongoing operations.

NIS2TISAXOT
Independence: We strictly separate consulting and auditing. Anyone who helped build your management system will not conduct your certification audit.
Experience

Faster to certification with experience from both sides of the audit

We know audits as consultants and as auditors. That is why we know what matters and bring your management system to certification readiness quickly.

25+Years of auditing and consultingwith a very large number of audits and assessments carried out
25+Years on standards committeesWe know requirements before they are published
Initial certificationVery high success rateOur clients usually achieve certification at the first attempt
Process maturityVery high maturity in the auditProcesses that convince auditors and assessors
More than 25 years of experience with security standards, from BS 7799 to today:ISO 27001ISO 27701TISAXNIST (US)SDMBSI IT-Grundschutz

Service: coordination with certification bodies

We maintain close contacts with certification bodies and handle the coordination for you.

  • Selecting the certification body and comparing quotes
  • Scheduling and audit plan
  • Communication during the audit
  • Follow-up on findings through to the certificate
Packages

The right model for your company

Every package includes the platform. You decide how much expert support to add.

Platform

For SMEs with their own CISO or DPO

Price on request
  • Expert and operational support for your internal CISO or DPO
  • All security and data protection modules
  • Standards-compliant templates and control catalogues
  • Onboarding workshop
  • Support from specialist consultants
Request a quote

Enterprise

For corporate groups, critical infrastructure and industry with OT

Individual quote
  • Multiple sites and entities
  • Integrated management systems
  • OT security according to IEC 62443
  • NIS2 and supply chain programmes
Get in touch

Add-on services for every package

External NIS2 OfficerExternal CISO (Information Security Officer)External DPO (Data Protection Officer)AI Officer under the AI Act and KI-MIGAI literacy training under Art. 4 AI ActNIS2 applicability checkInternal audits according to ISO 27001, 27701, 22301Supplier auditsCoordination with certification bodiesWhistleblowing system under the German Whistleblower Protection Act (HinSchG)TISAX consulting and assessmentOT assessment according to IEC 62443International legal monitoringAwareness trainingIT audit for the annual financial statements

Every package includes full access to the platform. The packages differ in how much expert support is included.

Expertise

Qualifications auditors recognise

Our consultants hold the internationally recognised ISACA certifications for audit, security, risk and governance.

CISACertified Information Systems Auditor
CISMCertified Information Security Manager
CRISCRisk and Information Systems Control
CGEITGovernance of Enterprise IT

What our experts take on for you

  • Officer roles as CISO, DPO or AI Officer, with formal appointment and annual planning
  • Building management systems from gap analysis to certification readiness
  • Internal audits and supplier audits with audit report and measure tracking in the tool
  • Security incidents: assess them and meet reporting obligations under NIS2 and GDPR
  • Changes to standards assessed early, for example the transition to ISO 27701:2025

One piece of evidence, several requirements

Example: your documented and audited access control is stored once in the platform and linked automatically.

ISO/IEC 27001:2022Annex A 5.15 Access control
NIS2 DirectiveArt. 21(2)(i)
GDPRArt. 32 Security of processing
ISO/IEC 27701PIMS extension of the controls
Downloads

Practical know-how to take away

Checklists and guides from our project and audit practice.

FAQ

Frequently asked questions

Answers on the platform, certification, packages, NIS2, KI-MIG, data protection and migrating from an existing ISMS.

Go to the FAQ
Peter Rentschler, Managing Director of CONSUVATION GmbH
Your contact
“Knowing both sides of the audit means knowing the shortest route to certification.”

Peter Rentschler

Managing Director, CONSUVATION GmbH

  • CISA · CISM · CRISC · CGEIT
  • Pioneer of BS 7799 auditing, the predecessor of ISO 27001
  • Contributes to the ISO standardisation committees for ISO 27001 and ISO 27701
  • More than 25 years of experience in auditing and consulting
Arrange a call

See the platform in 30 minutes

We show you the platform using your target standard as the example and discuss the shortest route to certification for you.

contact@consuvation.com
CONSUVATION GmbH · Tilsiter Str. 6 · D-71065 Sindelfingen · +49 (0) 7031.4181-860 · contact@consuvation.com